
What Are Data Security Examples and Why Do They Matter?
Data security examples show how individuals and organizations protect important information from unauthorized access, theft, loss, and misuse. These examples include password protection, data encryption, secure backups, and access controls. Understanding these practices helps people recognize common security risks and take practical steps to protect personal and business information in everyday situations.
Every time someone uses online banking, shops through a website, or shares information with a company, data security becomes important. Businesses collect customer names, payment details, addresses, and other sensitive records that require protection. Without suitable security measures, this information could become exposed through cyberattacks, employee mistakes, or poorly configured systems, potentially causing financial and reputational damage.
Learning about data security does not require advanced technical knowledge or cybersecurity experience. Many effective security practices involve simple actions, such as enabling additional account verification and keeping software updated. By exploring real-world data security examples, you can understand how different protective measures work together to reduce risks and maintain information privacy across digital environments.
Password Protection as a Basic Data Security Example
Password protection is one of the most familiar data security examples used across websites, applications, and business systems. A password helps verify that someone attempting to access an account has the required credentials. Strong, unique passwords reduce the risk of unauthorized access, particularly when attackers attempt to reuse passwords stolen from other websites or services.
For example, imagine an employee accessing a company’s customer management platform using a simple password shared across multiple accounts. If another website experiences a data breach, attackers could try those exposed credentials against the company’s system. Using a unique password for each account makes this type of attack less likely to succeed and limits potential damage.
Organizations often strengthen password security through password managers, account lockout protections, and secure authentication policies. Password managers help users create and store long, unique passwords without memorizing every credential. However, passwords alone cannot prevent every security incident, so combining them with additional verification methods provides stronger protection for sensitive information and important business applications.
Multi-Factor Authentication for Stronger Account Security
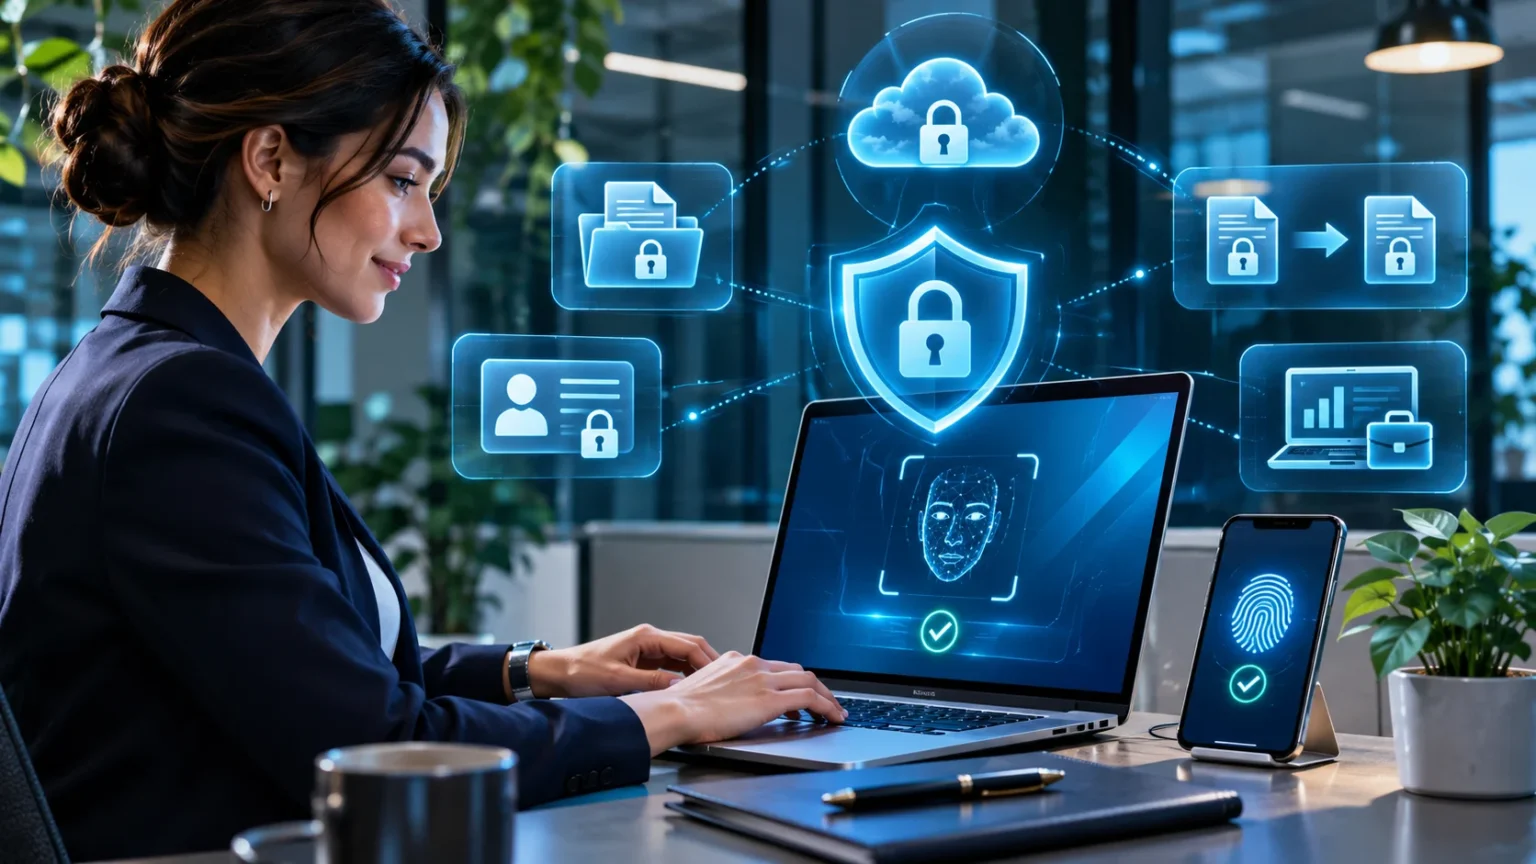
Multi-factor authentication, commonly called MFA, adds another security layer by requiring more than one type of verification. Instead of relying entirely on a password, a system may request a passkey, authenticator application approval, or another independent verification factor. This approach makes unauthorized access more difficult, particularly when an attacker already knows someone’s password.
Consider an employee attempting to access a company’s financial dashboard from a new device. After entering their password, the employee must approve the login through a registered authenticator application. Even if someone steals the account password, they may still be unable to enter without completing the additional verification process successfully.
MFA is particularly valuable for email accounts, cloud storage, financial platforms, and administrative systems. Organizations should prioritize phishing-resistant authentication methods, such as security keys and properly implemented passkeys, whenever practical. Although MFA cannot eliminate every cyber threat, it significantly strengthens identity verification and helps protect valuable information from common account compromise attacks.
Data Encryption Protects Sensitive Information
Data encryption is another important example of data security that protects information by converting it into an unreadable form. Authorized users or systems can restore the original information using appropriate cryptographic keys. Encryption helps protect sensitive records when stored on devices, transferred between systems, or exchanged through online communication channels.
A common example involves customers entering payment information on an online shopping website. When the website uses properly configured HTTPS connections, encryption protects information traveling between the customer’s browser and the website. This helps prevent outsiders from reading intercepted communication, although secure transmission alone does not guarantee that the website itself is trustworthy.
Businesses also use encryption to protect stored databases, employee devices, backups, and confidential documents. For example, full-disk encryption can help prevent someone from reading files on a lost laptop without proper authorization. Effective encryption also requires secure key management, appropriate permissions, and regular maintenance to ensure the protection remains reliable over time.
Access Control Limits Who Can View Company Data
Access control determines which people, devices, and applications can view or modify specific information within a system. Organizations use access permissions to ensure that employees only receive the information necessary for their responsibilities. This approach, known as the principle of least privilege, reduces unnecessary exposure and limits the potential impact of compromised accounts.
Imagine a company where customer support representatives need access to order histories but not employee salary records. Access control settings can allow support staff to view relevant customer information while restricting financial and human resources documents. Managers may receive broader permissions depending on their responsibilities, while system administrators manage access according to established organizational security policies.
Role-based access control is a common method for organizing permissions around job responsibilities. Companies can assign predefined access levels to departments rather than configuring every employee account individually. Reviewing permissions regularly is important because employees change roles, leave organizations, or receive temporary access that may no longer be appropriate for their duties.
Data Backup and Recovery Prevent Information Loss
Data backups provide additional copies of important information that organizations can restore when original files become unavailable. Information may be lost through accidental deletion, hardware failure, malicious activity, or unexpected technical problems. Reliable backup systems help organizations recover critical records and continue operating without depending entirely on their primary storage environment.
For example, a small business might accidentally delete several months of customer invoices from its accounting software. If the company maintains recent, verified backups, administrators may be able to restore the missing information. Without suitable backups, recovering those invoices could become expensive, time-consuming, or impossible, depending on how the original information was stored.
A practical backup strategy often includes multiple copies stored across different locations or storage systems. Organizations should consider keeping protected offline or immutable backups that attackers cannot easily modify or delete. Regular restoration testing is equally important because backups only provide meaningful protection when the information can actually be recovered when needed.
Email Security and Phishing Prevention in Real Life
Email security helps protect users from fraudulent messages, malicious attachments, and deceptive links designed to steal information. Phishing attacks often imitate trusted businesses, colleagues, or service providers to convince recipients to disclose credentials. Understanding suspicious communication patterns is an important part of protecting personal information and reducing the likelihood of business account compromise.
Imagine an employee receiving an email that appears to come from the company’s payroll department. The message asks them to open a link and confirm their login details immediately to prevent a payment delay. If the employee enters their password on a fraudulent website, attackers could capture the credentials and attempt unauthorized account access.
Organizations reduce phishing risks through spam filtering, email authentication technologies, employee awareness training, and multi-factor authentication. Employees should verify unexpected financial requests or account changes through a trusted communication channel. Reporting suspicious messages also helps security teams identify possible attacks and protect other employees who may receive similar emails.
Network Security Protects Connected Devices and Systems
Network security involves protecting devices, applications, and information that communicate through computer networks. Security measures help control traffic, identify suspicious connections, and restrict unauthorized access to important resources. Common examples include firewalls, secure wireless configurations, network segmentation, and intrusion detection systems used in homes, schools, and business environments.
A firewall provides a practical example by filtering network traffic according to established security rules. For instance, a business firewall may block unauthorized incoming connections while allowing employees to access approved online services. This helps reduce exposure to certain network threats, although firewalls cannot prevent every attack or replace other cybersecurity protections.
Network segmentation offers another useful example by separating sensitive systems from general-purpose devices. A company might isolate payment processing servers from its visitor Wi-Fi network to limit unnecessary connections. Secure network configurations, timely updates, and continuous monitoring work together to strengthen protection and make it harder for attackers to move between connected systems.
Endpoint Security for Laptops, Phones, and Computers
Endpoint security focuses on protecting devices that connect to company networks or access sensitive information. These devices include laptops, smartphones, desktop computers, and tablets used by employees. Because endpoints often store credentials and business documents, protecting them helps reduce the risk of malware infections, unauthorized access, and accidental information exposure.
Consider a remote employee using a laptop to access confidential company records while working outside the office. If the laptop becomes infected with malicious software, sensitive information could be exposed or business operations disrupted. Endpoint security tools can help detect suspicious behavior, block certain threats, and support administrators in responding to potential incidents.
Effective endpoint protection includes operating system updates, anti-malware tools, device encryption, and secure configuration settings. Businesses may also use centralized device management to enforce security requirements and remotely protect managed devices. Employees should avoid installing unapproved applications and report missing devices quickly so the organization can take appropriate protective measures.
Cloud Data Security Examples in Modern Businesses
Cloud data security involves protecting information stored or processed through internet-based computing services. Organizations increasingly use cloud platforms for collaboration, file storage, application hosting, and customer relationship management. These services offer flexibility, but businesses must still configure permissions, authentication, encryption, and monitoring correctly to protect sensitive information against unauthorized exposure.
For example, a marketing agency might store client campaign documents in a shared cloud folder. If the folder is accidentally configured for public access, confidential files could become available to people outside the organization. Restricting sharing permissions and regularly reviewing access settings helps prevent unintended exposure while allowing authorized team members to collaborate.
Cloud providers and customers generally share responsibility for different aspects of information security, depending on the service model. Providers typically secure underlying infrastructure, while customers manage responsibilities such as user permissions and data configurations. Understanding this division helps businesses avoid security gaps and select suitable protective controls for their cloud environments.
Data Loss Prevention Helps Stop Accidental Information Exposure
Data loss prevention, often shortened to DLP, refers to technologies and policies designed to reduce unauthorized information sharing. These systems can identify sensitive information and apply restrictions when users attempt certain actions. Businesses commonly use data loss prevention measures to protect customer records, financial documents, intellectual property, and confidential internal communications.
Imagine an employee accidentally attaching a spreadsheet containing customer payment details to an email intended for an external supplier. A properly configured DLP system may detect sensitive information and warn the employee or block the message. This additional safeguard can prevent some accidental disclosures before confidential records leave the organization’s controlled environment.
Data loss prevention tools may monitor email communication, cloud storage, and file transfers according to configured policies. However, automated detection is not perfect, and overly restrictive settings can interrupt legitimate work. Organizations should combine these technologies with clear classification rules, employee training, and periodic policy reviews to maintain effective information protection.
Security Monitoring and Incident Response in Action
Security monitoring involves observing systems, accounts, and network activities to identify unusual behavior or potential security incidents. Organizations collect relevant activity logs and use monitoring tools to detect suspicious events. These alerts can help security professionals investigate possible threats before attackers cause additional damage or gain broader access to sensitive information.
For example, a company’s monitoring system might identify repeated unsuccessful login attempts followed by an unusual successful connection. Security personnel can investigate whether the activity represents a legitimate user or a compromised account. Depending on the findings, the organization may temporarily restrict access, require additional verification, or examine related activity for further warning signs.
Incident response provides a structured approach for handling confirmed or suspected security problems. A response plan typically covers preparation, detection, containment, recovery, and lessons learned after an incident. Companies that establish responsibilities and practice response procedures can make more informed decisions during disruptions and improve their ability to restore normal operations safely.
Employee Training and Security Policies Reduce Human Errors
Employee training is an essential part of data security because technical systems cannot prevent every human mistake. Staff members regularly handle passwords, confidential files, customer information, and business communications. Teaching employees how to recognize risks and follow protective procedures helps create a workplace where information security becomes part of everyday responsibilities.
For example, an organization may train employees to recognize suspicious login requests, verify unusual payment instructions, and report potentially exposed information. Regular training sessions can use realistic workplace scenarios rather than complicated technical explanations. This approach helps employees understand the consequences of unsafe actions and identify appropriate responses when unexpected situations occur.
Written security policies support training by establishing consistent expectations for information handling and system access. These policies may cover password management, approved devices, document sharing, remote work, and incident reporting. Organizations should review policies periodically and make them accessible, practical, and understandable so employees can follow them without unnecessary confusion.
How to Apply Data Security Practices in Everyday Life
Applying data security practices begins with identifying which personal or business information requires protection. Financial accounts, private messages, identity documents, and confidential workplace records deserve particular attention. Understanding where information is stored, who can access it, and how it is shared helps individuals select appropriate security measures for their circumstances.
For personal accounts, useful steps include creating unique passwords, enabling multi-factor authentication, updating software, and protecting mobile devices with secure screen locks. Regularly reviewing account activity can also reveal unfamiliar access attempts or unexpected changes. When handling sensitive information, using trusted services and checking sharing permissions provides additional protection against accidental exposure.
Businesses should take a broader approach by combining preventive measures with monitoring, backups, and clear recovery procedures. Regular risk assessments help identify weaknesses and prioritize improvements based on potential consequences. Data security works best as an ongoing process because technology, employee responsibilities, and cyber threats continually change rather than remaining fixed over time.
Conclusion
Understanding real-world data security examples makes cybersecurity easier to recognize and apply in everyday situations. Password protection, encryption, multi-factor authentication, and access controls help prevent unauthorized access to important information. Meanwhile, backups, monitoring, and incident response procedures help organizations prepare for unexpected security problems and recover more effectively when disruptions occur.
No single security tool can protect every account, device, or business system from every possible threat. Strong protection requires multiple complementary safeguards, along with regular software updates, responsible information handling, and appropriate employee training. Combining these measures reduces avoidable risks and supports a more reliable approach to protecting sensitive information.
Whether you manage a business or simply want to protect your personal accounts, small security improvements can make a meaningful difference. Begin with practical measures that address your most important risks, then review them regularly. By applying these data security examples consistently, you can build stronger digital protection and maintain greater confidence when using online services.
Frequently Asked Questions (FAQs)
What are five common examples of data security?
Five common data security examples are encryption, password protection, multi-factor authentication, access control, and regular data backups. These measures help protect sensitive information against unauthorized access, accidental loss, and various cybersecurity threats.
What is the difference between data security and data privacy?
Data security protects information against unauthorized access, alteration, and loss, while data privacy focuses on how personal information is collected, used, and shared. Both are important for responsible information management.
Why is data encryption important for businesses?
Data encryption helps businesses protect confidential information by making it unreadable without appropriate cryptographic keys. It reduces exposure risks when sensitive records are stored on devices or transmitted through networks.
How can small businesses improve data security?
Small businesses can improve data security through unique passwords, multi-factor authentication, regular backups, software updates, and employee training. Restricting access to sensitive information and reviewing security settings also help reduce risks.
What is the most important data security practice?
There is no single security practice that addresses every threat. Strong protection usually combines multi-factor authentication, secure passwords, encryption, backups, access controls, and regular monitoring based on the information and systems being protected.