
What Is HSM in Cyber Security?
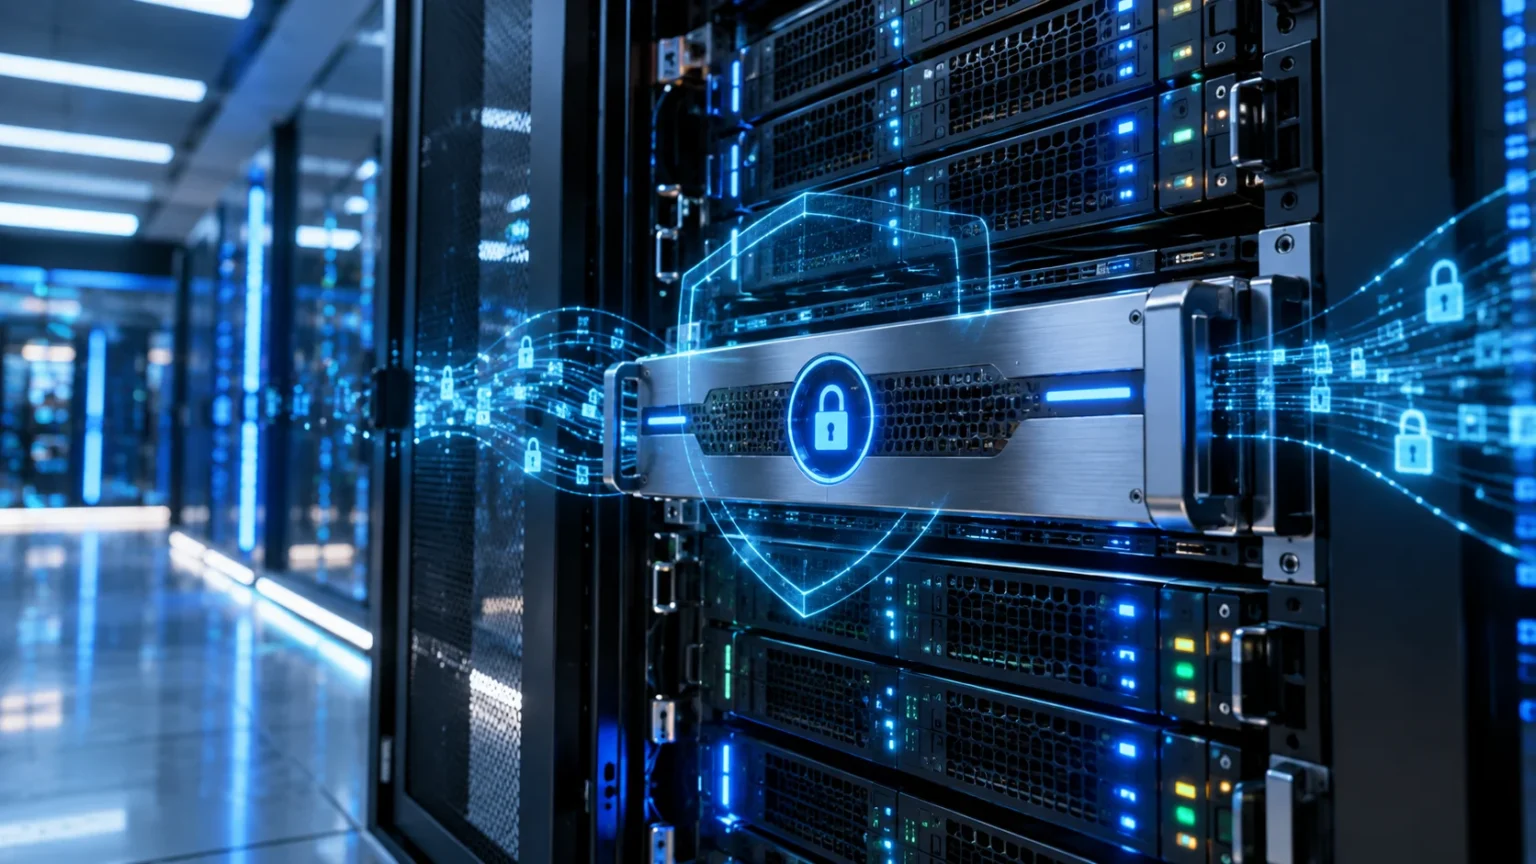
HSM stands for Hardware Security Module, a specialized security device designed to protect sensitive cryptographic keys and perform important encryption-related operations. Unlike ordinary software-based security controls, an HSM uses dedicated hardware with strong protection mechanisms. It helps organizations secure digital identities, encryption keys, payment data, certificates, and other information that requires strict access control.
In cybersecurity, an HSM acts as a highly protected environment for cryptographic operations. Private keys can remain inside the device while encryption, decryption, signing, and verification occur within its protected boundaries. This approach reduces the risk of exposing critical keys to operating systems, applications, databases, or other parts of an IT environment.
HSM technology is widely used in banking, cloud computing, telecommunications, government systems, healthcare, and enterprise security. It is particularly useful when an organization must meet strict security requirements while maintaining control over cryptographic material. By combining tamper resistance, access controls, key management, and cryptographic processing, an HSM strengthens the foundation of a cybersecurity architecture.
How Does an HSM Work?
An HSM works by securely storing cryptographic keys and carrying out approved cryptographic operations inside a protected hardware environment. An application sends a request to the module through an authorized interface, while the sensitive key remains within the protected boundary. The HSM then performs the required operation and returns the resulting cryptographic output.
A typical HSM uses authentication, authorization policies, secure key storage, cryptographic algorithms, and tamper detection to protect its internal functions. Access can be restricted according to users, applications, roles, or administrative policies. When suspicious physical or logical activity is detected, the device can respond according to its configured security controls.
The exact workflow depends on the organization’s security architecture and the HSM’s intended role. For example, a payment system may use an HSM to protect card-related cryptographic keys, while a certificate authority may rely on one to safeguard private signing keys. In both cases, the central principle remains the same: sensitive cryptographic material stays under controlled hardware protection.
Why Are HSMs Important in Cybersecurity?
Cryptographic keys are among the most sensitive assets in a modern security environment. If an attacker obtains a private encryption key, certificate key, or signing key, the consequences can extend far beyond a single compromised account. HSMs help reduce this exposure by keeping important keys inside a dedicated security boundary rather than leaving them broadly accessible to software.
HSMs also strengthen trust in digital transactions and machine-to-machine communication. Digital signatures, encrypted connections, authentication systems, payment processes, and certificate infrastructure can depend on cryptographic keys that require strong protection. When these keys are managed through dedicated hardware, organizations gain additional safeguards against unauthorized extraction and misuse.
Another important benefit is support for security governance and compliance requirements. Many regulated environments need strict controls around key generation, storage, access, rotation, and retirement. An HSM can support these processes through controlled administrative functions, audit capabilities, and hardware-backed security mechanisms, helping organizations maintain stronger oversight of cryptographic assets.
Key Features of a Hardware Security Module
One major HSM feature is secure cryptographic key storage. Instead of keeping sensitive keys in ordinary files, databases, or application memory, the device stores them inside a controlled hardware environment. This reduces the number of places where high-value cryptographic material can be exposed during normal system operation or a security incident.
Tamper resistance is another important capability. HSMs can include mechanisms that detect attempts to physically access or manipulate protected components. Depending on the device and security configuration, a detected tampering event can trigger protective responses designed to prevent unauthorized access to sensitive cryptographic material.
Strong access management is also central to HSM security. Administrative controls can separate responsibilities between different users and restrict sensitive operations according to defined permissions. Many enterprise environments also rely on logging, authentication, secure interfaces, key lifecycle controls, and policy enforcement to maintain accountability over cryptographic operations.
HSM vs Software-Based Key Storage
Software-based key storage can be practical for many applications, but it may expose cryptographic keys to operating systems, application processes, memory, backups, or administrators. An HSM places stronger boundaries around critical key material by keeping it within dedicated hardware. This distinction becomes especially important when a key protects highly sensitive systems or high-value transactions.
Another difference involves resistance to key extraction. A software key may ultimately exist as data that can be copied if an attacker gains sufficient access to the host environment. HSMs are designed so that sensitive keys normally remain inside the device while cryptographic operations take place internally. This architecture can significantly reduce direct exposure of private keys.
The two approaches can also work together rather than being viewed as complete substitutes. Applications may use ordinary software mechanisms for lower-risk cryptographic tasks while relying on HSMs for the most sensitive keys. The appropriate design depends on risk, regulatory requirements, performance needs, infrastructure complexity, and the value of the assets being protected.
Common Uses of HSM in Cyber Security
HSMs are frequently used to protect private keys associated with digital certificates and public key infrastructure. Certificate authorities can rely on hardware-backed key protection when signing certificates or managing other sensitive PKI operations. This helps maintain confidence in digital identities and reduces the risk associated with unauthorized access to certificate authority keys.
Financial institutions also use HSM technology for payment security and transaction processing. Payment environments can require cryptographic operations involving payment cards, transaction authentication, PIN protection, and secure message processing. Because these systems handle highly sensitive financial information, dedicated hardware protection can play an important role in reducing cryptographic key exposure.
HSMs are also relevant to cloud security, database encryption, code signing, tokenization, identity management, and secure application infrastructure. Organizations may use them wherever a private key, signing key, master encryption key, or other cryptographic secret requires stronger protection. Their role is therefore broader than simply encrypting files or network traffic.
HSM and Encryption Key Management
Effective encryption depends heavily on how cryptographic keys are handled throughout their lifecycle. Key management includes generation, storage, access, rotation, backup, recovery, suspension, and retirement. An HSM can act as a trusted foundation for these activities by keeping high-value keys within a controlled hardware environment.
Key generation is particularly important because weak or poorly handled keys can undermine otherwise strong encryption algorithms. HSMs can use approved cryptographic processes and secure sources of randomness for key generation. Once generated, sensitive keys can remain inside the device, reducing unnecessary movement of key material across networks or application environments.
Key rotation is another important part of cryptographic hygiene. Organizations may periodically replace encryption or signing keys because of policy requirements, risk considerations, system changes, or defined cryptoperiods. With appropriate HSM integration, key lifecycle operations can be governed through established policies while reducing the chance of accidental exposure during routine administration.
Types of HSMs
Network HSMs are dedicated devices that can serve multiple applications across an organization’s infrastructure. They are commonly positioned within protected data center environments and accessed through controlled network connections. This architecture can suit organizations that need centralized cryptographic services for several applications, systems, or business functions.
Cloud HSM services use dedicated or isolated hardware security capabilities within cloud environments. They can support organizations that have moved workloads to cloud infrastructure but still require hardware-backed protection for important cryptographic keys. Depending on the service architecture, administrators can manage cryptographic resources through cloud interfaces while maintaining stronger protection for sensitive key material.
Payment HSMs are specialized for financial transaction environments and payment-related cryptographic requirements. They can support operations associated with payment cards, transaction authentication, PIN security, and other financial processes. Beyond these categories, organizations may encounter HSMs designed for specific enterprise, certificate authority, code-signing, or high-assurance security workloads.
Benefits of Using an HSM
One important benefit of HSM technology is stronger protection for high-value cryptographic keys. Keeping sensitive keys inside dedicated hardware can reduce exposure compared with storing them directly within application servers or ordinary storage systems. This becomes especially valuable when keys support identity systems, financial transactions, certificate authorities, or critical encryption infrastructure.
HSMs can also support separation of duties and stronger administrative control. Sensitive cryptographic actions can require authenticated administrators, defined permissions, multiple authorized personnel, or carefully governed procedures. These controls can reduce the likelihood that one compromised account or careless administrative action will expose an organization’s most important cryptographic assets.
Another benefit is improved security assurance for environments with demanding compliance expectations. HSMs can support documented security processes around cryptographic key handling, access management, auditing, and lifecycle management. Their value, however, depends on correct configuration and operational discipline because hardware alone cannot compensate for weak policies, excessive privileges, poor monitoring, or insecure application integration.
Challenges and Limitations of HSMs
HSMs can involve higher costs and greater operational complexity than basic software-based key storage. Organizations may need specialized hardware, trained personnel, secure deployment procedures, maintenance processes, and carefully designed integration. These requirements can be significant for smaller environments where the protected information does not justify the additional infrastructure.
Performance and availability also require careful planning. Cryptographic operations may pass through an HSM, so applications that depend heavily on cryptographic processing need suitable capacity and redundancy. Organizations may use clustered or replicated configurations where appropriate to reduce service interruptions and maintain access to essential cryptographic functions during hardware failures or maintenance.
HSM security also depends on proper administration. Poor access controls, weak authentication, incorrect backup procedures, exposed management interfaces, or flawed application integration can undermine the intended protection. A successful HSM strategy therefore combines secure hardware with strong policies, trained administrators, monitoring, incident response procedures, and regular security reviews.
HSM Security Best Practices
Organizations should begin by identifying which cryptographic keys require hardware-backed protection and why those keys matter. Not every encryption key necessarily needs an HSM, so risk assessment should guide the architecture. Priority commonly goes to keys associated with financial transactions, certificate authorities, critical identities, sensitive databases, code signing, and other high-impact security functions.
Access to HSM administration should follow strict privilege management principles. Administrative accounts should use strong authentication, limited permissions, secure management channels, and appropriate separation of responsibilities. Organizations should also monitor administrative activity and maintain reliable audit records so unusual actions can be investigated quickly.
HSM deployments should include resilience and recovery planning from the beginning. Backup procedures, disaster recovery arrangements, key recovery policies, firmware management, certificate dependencies, and replacement procedures should be documented and tested. Regular security assessments can then identify configuration weaknesses, outdated processes, excessive privileges, or architectural changes that may affect the protection of cryptographic assets.
HSM in Cloud Security
Cloud environments have increased the need for flexible protection of encryption keys and digital identities. Cloud HSM capabilities can help organizations maintain hardware-backed cryptographic protection while running applications on cloud infrastructure. This can be useful for workloads that require stronger control over keys used for encryption, signing, authentication, or certificate management.
A cloud HSM can also support separation between application workloads and cryptographic key protection. Applications may interact with cryptographic services through controlled interfaces while sensitive keys remain within protected hardware. This arrangement can reduce the need to place important private keys directly inside virtual machines, containers, application code, or ordinary cloud storage.
Cloud adoption does not remove the need for careful security design. Organizations still need to evaluate identity permissions, network access, logging, availability, key lifecycle policies, recovery procedures, and provider responsibilities. A strong cloud security architecture treats HSM capabilities as one component within a broader strategy involving encryption, identity security, access management, monitoring, and incident response.
HSM and Public Key Infrastructure
Public Key Infrastructure, commonly called PKI, depends on cryptographic keys to establish trusted digital identities. Certificate authorities use private keys to sign digital certificates, making protection of those keys extremely important. An HSM can safeguard certificate authority keys and perform signing operations without exposing the private key directly to ordinary server environments.
This protection is particularly important for root and intermediate certificate authorities. If a high-level certificate authority key is compromised, attackers may gain the ability to misuse digital trust relationships or issue unauthorized certificates. Hardware-backed key protection can therefore strengthen the security boundary around the most sensitive components of a PKI architecture.
HSMs can also support certificate lifecycle processes across enterprise environments. Digital certificates may secure websites, applications, APIs, devices, services, and internal systems. By protecting the cryptographic keys behind those certificates, HSM technology helps organizations maintain stronger control over digital identity and trust infrastructure.
HSM Compliance and Security Standards
Security standards and regulatory requirements can influence whether an organization adopts HSM technology. Financial services, payment environments, government systems, and other regulated sectors may face specific expectations concerning cryptographic key protection. An HSM can support these requirements through controlled key handling, secure administrative functions, audit capabilities, and tamper-resistant hardware.
Some HSMs are evaluated against recognized security standards or certification programs. The exact certification depends on the device, model, configuration, and intended use. Organizations should therefore examine the security requirements that apply to their environment rather than assuming that every HSM automatically satisfies every regulatory or compliance obligation.
Compliance should also be treated as part of a wider security program. An HSM does not independently make an organization secure or compliant. Policies, access controls, documentation, monitoring, personnel procedures, application architecture, incident response, and regular assessments remain important parts of a defensible cybersecurity framework.
Conclusion
An HSM in cybersecurity is a specialized hardware security device designed to protect sensitive cryptographic keys and perform cryptographic operations within a controlled environment. It can strengthen encryption, digital signatures, payment security, certificate management, identity systems, and other security functions that depend on trusted keys.
The main value of an HSM comes from reducing direct exposure of high-value cryptographic material. Its security capabilities can support stronger access control, tamper resistance, key lifecycle management, auditing, and compliance-focused security practices. However, successful deployment still requires thoughtful architecture, disciplined administration, resilience planning, and continuous security oversight.
For organizations handling sensitive transactions, critical identities, regulated information, or high-value encryption keys, HSM technology can become an important part of a mature cybersecurity strategy. Understanding how HSMs work and where they fit allows security teams to make more informed decisions about key protection, cryptographic infrastructure, and long-term risk management.
Frequently Asked Questions About HSM in Cyber Security
What does HSM stand for in cybersecurity?
HSM stands for Hardware Security Module. It is a specialized security device that protects cryptographic keys and performs operations such as encryption, decryption, digital signing, and verification inside a protected hardware environment.
What is the main purpose of an HSM?
The main purpose of an HSM is to protect sensitive cryptographic keys from unauthorized access or extraction. It also performs approved cryptographic operations while keeping important private keys within its protected security boundary.
Is an HSM used for encryption?
Yes, HSMs can support encryption and decryption operations, but their role extends beyond encryption. They can also protect signing keys, support authentication, manage certificates, safeguard payment transactions, and strengthen public key infrastructure.
Are HSMs used in cloud computing?
Yes. Cloud HSM services can give organizations hardware-backed cryptographic protection while their applications run in cloud environments. They are commonly used for encryption keys, certificate authorities, digital signatures, identity systems, and sensitive workloads.
Is an HSM necessary for every organization?
Not every organization needs an HSM. Its value depends on factors such as risk level, regulatory requirements, sensitivity of cryptographic keys, transaction volume, security architecture, and the consequences of key compromise.